
stage 4 of the engagement
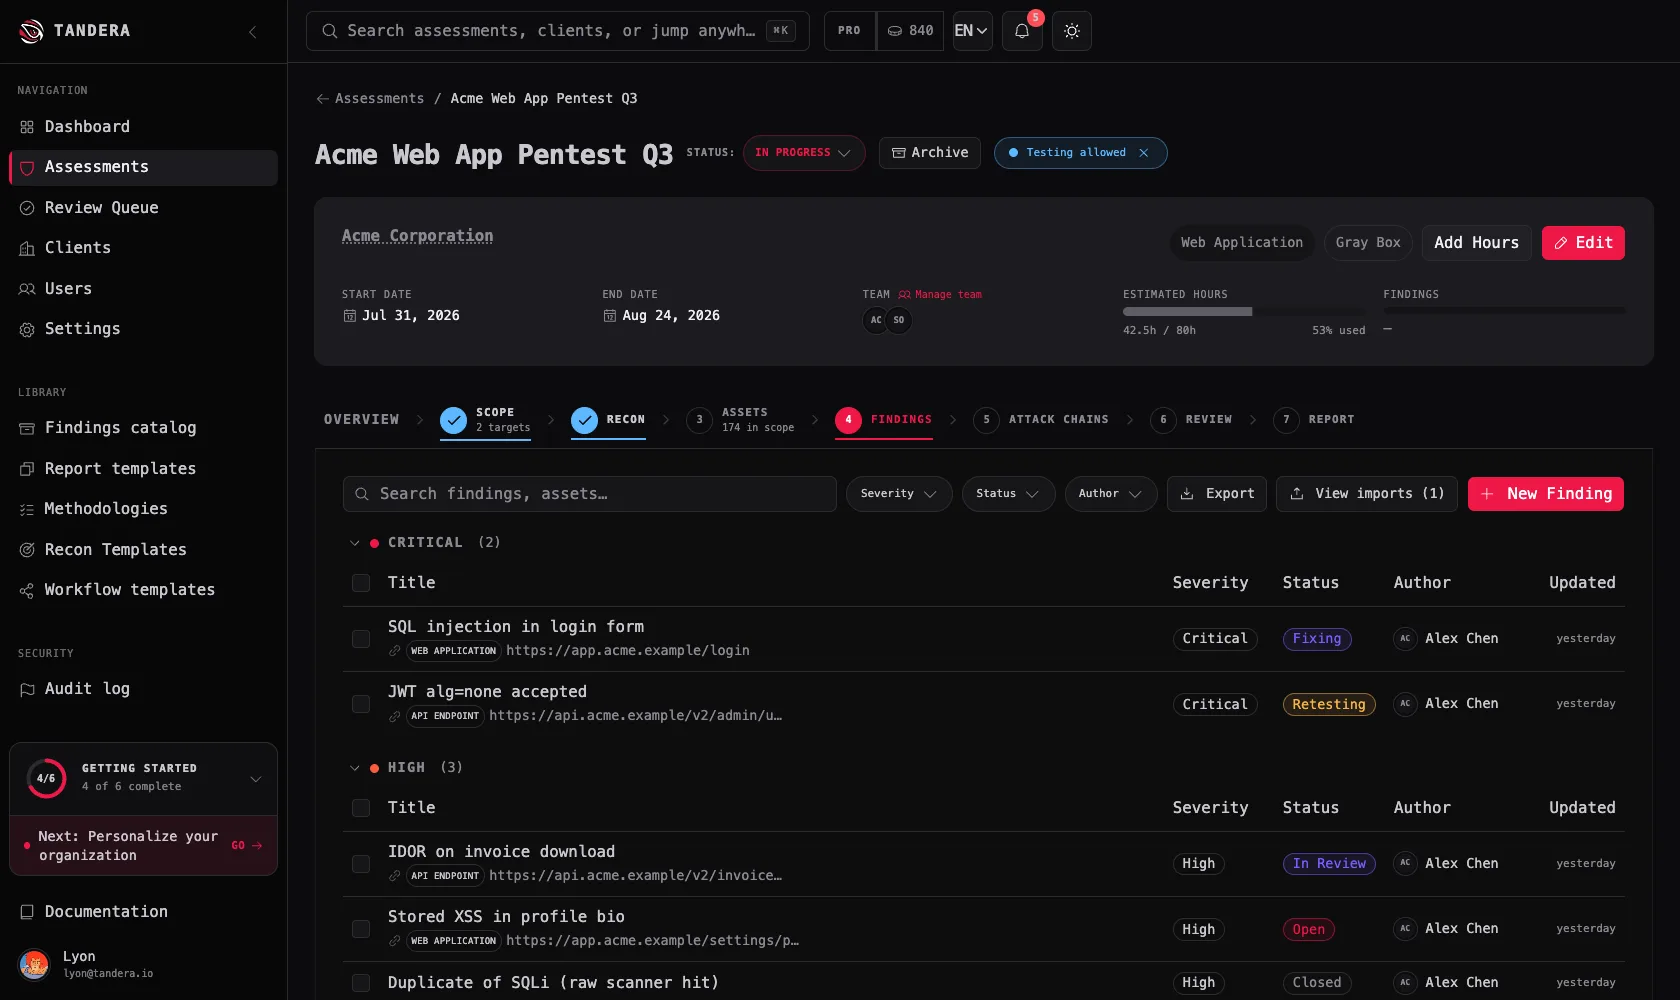
One finding per issue, whichever tool found it
Import from the scanners your team already runs, then correlate what they report into a single finding per issue. Each tool’s evidence is kept and attributed. Manual findings sit in the same list, in the same shape.
02 · CENTRALIZED FINDINGS
One source of truth for every vulnerability.
Each vulnerability becomes a structured, deduplicated, correlated finding. Severity, CVSS, EPSS, KEV, CWE, CVE, OWASP, MITRE, compliance, evidence, and provenance travel with it.
Severity
Finding
CVSS
Source
CRIT
SQL injection · /api/login
9.8
nuclei
HIGH
Exposed .git directory
8.2
recon
MED
Missing security headers ×3 merged
5.3
burp
LOW
Verbose error message
3.1
zap
EPSSKEVCWEOWASPMITRE ATT&CKcompliance
03 · IMPORTERS
Bring your own tools.
We ingest Burp Suite, Nuclei, OWASP ZAP, Caido, and generic CSV. Everything normalizes into the same table.
Burp Suite✓ .xml
Nuclei✓ .json
OWASP ZAP✓ .json
Caido✓ export
Generic CSV✓ .csv
When three tools report the same issue, you get one finding. Each tool’s evidence is kept and attributed to its source.
Import from 202 security tools
Generated from our parser registry, not a marketing number. See the full list.
 Burp Suite
 Nuclei
 OWASP ZAP
 Nessus
 Acunetix
 Nmap
 Nikto
 Snyk
 Trivy
 TruffleHog Burp Suite Nuclei OWASP ZAP Nessus Acunetix Nmap Nikto Snyk Trivy TruffleHog
The rest of the engagement
Every stage writes to the same engagement record.
early access
Get Tandera before your next engagement.
Join the waitlist for early access. We are onboarding pentest teams in waves.
✓Priority onboarding for pentest teams.
✓A direct line to the people building it.
✓Early-access pricing, locked in.
No spam, no card. Unsubscribe anytime.